The challenge
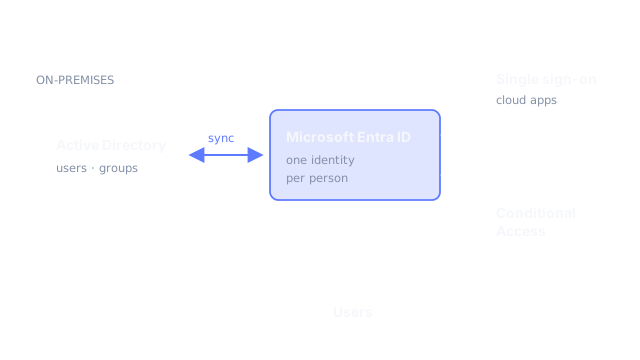
On-premises and cloud identities were managed separately. That meant separate accounts and passwords to look after, more work every time someone joined, changed role or left, and no single place to apply sign-in security across both worlds.
The objective
- One identity per person across on-premises and cloud services.
- Single sign-on to cloud applications.
- Simpler user lifecycle management.
- Stronger sign-in security through Conditional Access.
What was delivered
- Hybrid identity environmentOn-premises Active Directory linked with Microsoft Entra ID (then Azure AD).
- Single sign-onSingle sign-on for users across connected applications.
- Conditional AccessConditional Access policies applied to cloud sign-ins.
- Simplified lifecycleA simplified process for managing users from joining to leaving.
Security considerations
Bringing identities together created one place to enforce sign-in rules. Conditional Access policies were used to strengthen security on cloud sign-ins, and a cleaner lifecycle process reduces the risk of accounts staying active after people leave.
Result
OUTCOME 01
Unified user management and authentication across on-premises and cloud.
OUTCOME 02
Single sign-on in place for users.
OUTCOME 03
Simpler user lifecycle management.
OUTCOME 04
Enhanced security through Conditional Access policies.