The challenge
Healthcare organisations handle sensitive data and can't afford to discover a security incident late. Security signals generated across many separate systems are hard to act on until they're collected, correlated and watched in one place.
The objective
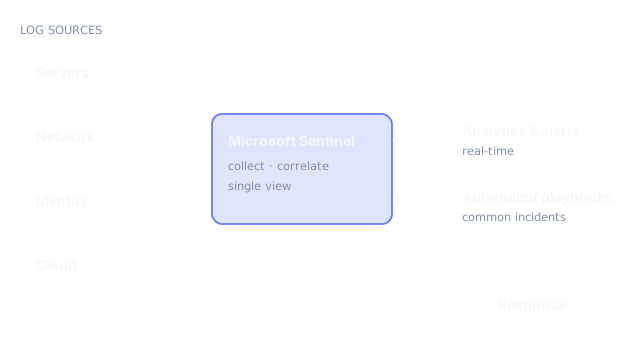
- Centralise threat monitoring and analysis.
- Detect threats in real time and assess security posture continuously.
- Automate the response to common security incidents.
What was delivered
- Security operations on SentinelSecurity operations capability implemented on Microsoft Sentinel.
- Centralised monitoringCentralised threat monitoring and analysis.
- Real-time postureReal-time security posture assessment.
- Automated playbooksAutomated response playbooks for common security incidents.
Security considerations
Automated playbooks shorten the time between detection and response for routine incidents, which leaves people free to focus on the alerts that need judgement. Centralised monitoring also gives a continuous view of security posture rather than a point-in-time snapshot.
Result
OUTCOME 01
Threat monitoring and analysis centralised in one platform.
OUTCOME 02
Real-time detection and continuous posture assessment.
OUTCOME 03
Common incidents handled by automated playbooks.