The challenge
Traditional security assumes that anything inside the network can be trusted. With users, devices and data spread across cloud and on-premises systems, that assumption no longer holds, and threats need to be detected across all of those places together rather than one system at a time.
The objective
- Base access on verified identity, not network location.
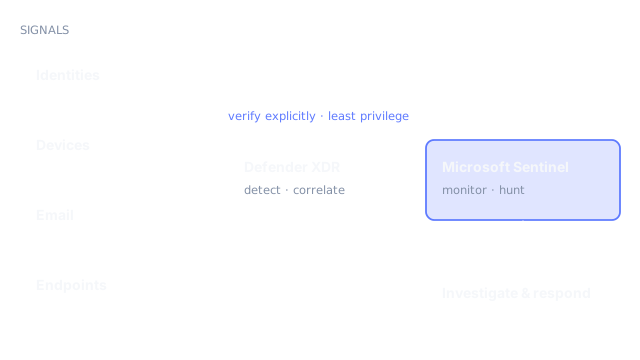
- Detect threats across identities, devices, email and endpoints in one place.
- Monitor continuously and automate response to common threats.
What was delivered
- Zero Trust frameworkA Zero Trust security framework designed and implemented for the environment.
- Identity-based accessIdentity-based access controls across cloud and on-premises systems.
- Integrated XDR detectionAdvanced threat detection with integrated Microsoft Defender XDR.
- Continuous monitoringContinuous monitoring and automated response in Microsoft Sentinel.
Security considerations
Zero Trust rests on three principles: verify explicitly, use least-privilege access, and assume breach. Identity-based access controls address the first two; integrated detection, continuous monitoring and automated response address the third.
Result
OUTCOME 01
Access controlled by identity across cloud and on-premises systems.
OUTCOME 02
Improved threat detection through integrated XDR.
OUTCOME 03
Continuous monitoring with automated response in place.